ARTICLE · 1288478
Cursor 插件商城曝 Claude Code 供应链后门
Cursor 插件商城曝 Claude Code 供应链后门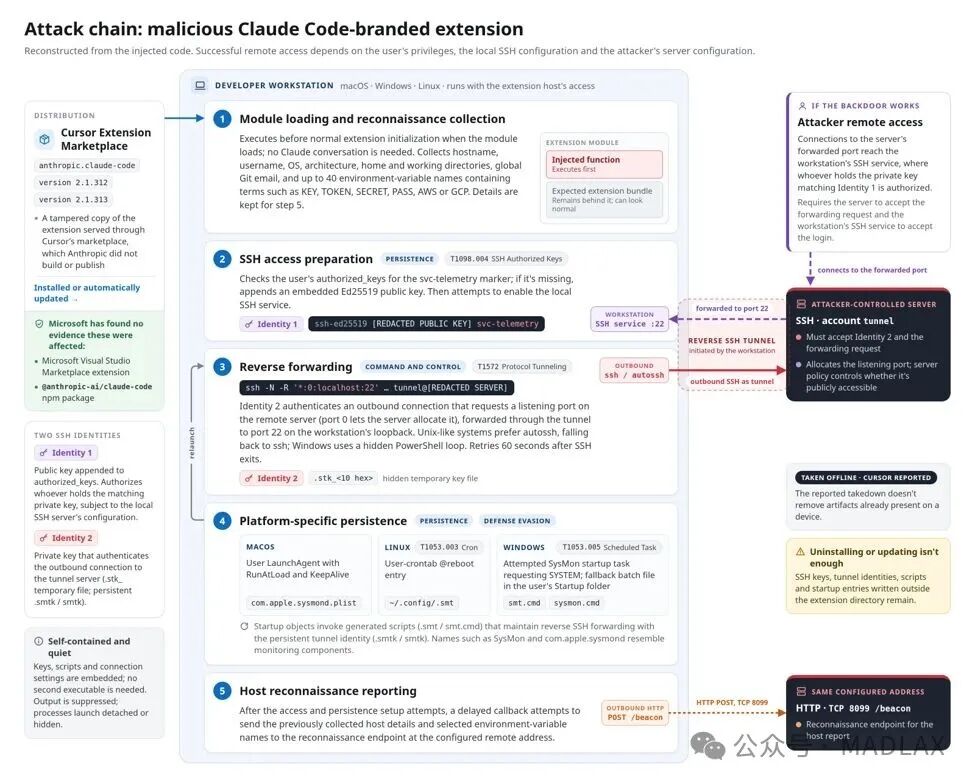 微软安全博客披露,10 月 29 日约 02:27–13:35(美西时间)Cursor 扩展市场出现被篡改的 anthropic.claude-code 2.1.312/2.1.313 扩展,在 extension.js 开头植入恶意加载器以安装持久 SSH 后门——采集主机名、用户名、Git 邮箱与公网 IP 并回传、向 authorized_keys 注入攻击者公钥、建立反向隧道,用 macOS LaunchAgent 或 Windows 计划任务做持久化。影响约 5,000 名开发者、持续约 11 小时;微软确认该包从未发布到 VS Marketplace 与 npm、Anthropic 系统未被攻破,Cursor 已下架扩展并临时关闭整个扩展市场轮换密钥。
来源: https://www.microsoft.com/en-us/security/blog/2026/10/30/inside-malicious-claude-code-branded-cursor-extension-persistent-ssh-backdoor/
微软安全博客披露,10 月 29 日约 02:27–13:35(美西时间)Cursor 扩展市场出现被篡改的 anthropic.claude-code 2.1.312/2.1.313 扩展,在 extension.js 开头植入恶意加载器以安装持久 SSH 后门——采集主机名、用户名、Git 邮箱与公网 IP 并回传、向 authorized_keys 注入攻击者公钥、建立反向隧道,用 macOS LaunchAgent 或 Windows 计划任务做持久化。影响约 5,000 名开发者、持续约 11 小时;微软确认该包从未发布到 VS Marketplace 与 npm、Anthropic 系统未被攻破,Cursor 已下架扩展并临时关闭整个扩展市场轮换密钥。- Module loading and reconnaissance collection.
The injected function executes before normal extension initialization and collects host and user information. - SSH access preparation.
The loader appends an embedded public key and attempts to enable the local SSH service. - Reverse forwarding.
An embedded tunnel identity authenticates an outbound connection that requests forwarding to the workstation’s SSH port. - Platform-specific persistence.
Scripts and startup configuration are written to relaunch the connection. - Host reconnaissance reporting.
After the access and persistence setup attempts, a delayed callback attempts to transmit the previously collected host details and selected environment-variable names.