ARTICLE · 1038789
AI 红队工具复盘:5 款停更,12 款新上榜
「strix 是不是得换上?我们那张表还能用吗?」这周一个工程师问我。
他说的那张表,是 5 月 9 号那篇AI 红队工具怎么选? 6 类 18 款对比。当时也是他私信来的,说老板让他下周交工具选型表,能不能把 repo 里那堆工具画张图分个类。
我把 5 月那 18 款重新拉了一遍 GitHub 数据。结果是:strix 这一个仓库,60 天涨了 20,755 星,比那 18 款里除 LiteLLM 和 langfuse 之外的 16 款 4 个月增量加起来(19,412)还多。而那 18 款里,有 5 款已经超过半年没有提交过代码。
5 月那张表不能直接用了。这篇把两张表并排放:旧表 4 个月后的变化,新上榜 12 款的定位和一条命令,再加上 7 月一篇论文给出的选型规则。
先说规矩:下面所有工具都只在授权范围内用。你自己的应用、自己的靶场、拿到书面授权的目标,其他一律不算。
5 月那 18 款现在怎么样了
先看老表。类别沿用 5 月的分法,数字是 5 月 9 日和 9 月 19 日两次 star 数,最后提交取仓库的 pushed_at。
停更的判定口径只有一条:pushed_at 距今超过 180 天。Portkey 的最后提交是 5 月 25 日,差一个多月才到线,所以列观察。
4 个月里涨得最多的是 LiteLLM 加了 12,998,langfuse 加了 7,997,promptfoo 加了 4,309。涨幅比例最大的是腾讯的 AI-Infra-Guard,从 3,650 到 6,453,翻了 1.77 倍。
5 款停更的名单和替代品
停更的 5 款分别是 FuzzyAI、promptmap、agentic-radar、MCP-Security-Checklist、AI-Red-Teaming-Playground-Labs。
停更的工具还能装,但有两件事要重新算。一是漏洞库和攻击样本不再更新,用 promptmap 这类扫描器扫 2026 年的应用,它的仓库最后一次提交停在 2025 年 12 月。二是依赖不再跟着升级,装的时候大概率要自己解决版本冲突。
对应的替代品,按 5 月的类别对上:
FuzzyAI 和 promptmap 做的事,模型层模糊测试和自定义 LLM 应用扫描,现在 garak 和 deepteam 都在做,两者最后提交分别是 9 月 16 日和 8 月 21 日。garak 装一条命令 pip install -U garak,deepteam 是pip install -U deepteam,它的 README 写明「runs locally on your machine」,建在 DeepEval 上。agentic-radar 做的 Agent 工作流扫描,snyk/agent-scan 覆盖了,而且加上了 MCP 配置和技能文件: uvx snyk-agent-scan@0.5.17 ~/.vscode/mcp.json扫 MCP 配置,uvx snyk-agent-scan@0.5.17 ~/path/to/my/SKILL.md扫技能。MCP-Security-Checklist 是一份清单,不是工具,慢雾 2025 年 4 月之后没更新。要清单的话,OWASP 那套标准更新得勤,后面单独说。 Playground-Labs 是微软的红队训练靶场,最后提交在 2 月 13 日。练手可以继续用,只是 2 月之后出现的技能供应链这类攻击面,它的题目里没有。
60 天涨最快的 10 个仓库
这张表来自我自己的快照,覆盖 ai-security、llm-security、red-teaming、pentesting、bug-bounty、prompt-injection、evaluation、benchmark 这几个 topic 的 top30。
两个说明。一,star 只反映关注度,iFixAi 60 天涨 13,956 星不代表它比 garak 好用,两者做的根本是两件事。二,这个榜只统计进了 topic top30 的仓库,openai/codex-security 30 天涨了 812 星,但 60 天前的快照里还没有它,所以没进前十。
自主 AI 渗透 Agent:strix、Shannon、PentAGI、CyberStrike
这是 5 月那张表里没有的类别。5 月的进攻侧只有 CAI 和 PentestGPT 这种框架,你得自己搭流程。这一类的定位是把整个渗透流程交给 Agent 跑完。
strix(Apache-2.0,63,580 星,https://github.com/usestrix/strix)。README 的原话是 「autonomous AI penetration testing agents that act just like real hackers - they run your code dynamically, find vulnerabilities」,强调 「Real exploit validation - working PoCs, not false positives」。运行方式是对着目录跑:
strix --target ./app-directory 它还能装成技能给 Claude Code、Cursor、Codex 用:npx skills add usestrix/strix。最后提交 9 月 18 日。
Shannon(AGPL-3.0,48,140 星,https://github.com/KeygraphHQ/shannon)。README 原话:「an autonomous, AI pentester for web applications and APIs. It analyzes your source code, identifies attack paths, and executes real exploits」。开源版就是完整 Agent,本地跑:
npx @keygraph/shannon@latest 注意 license 是 AGPL,公司内部用没问题,要集成进对外产品得看法务。最后提交 9 月 8 日。
PentAGI(MIT,24,722 星,建于 2025 年 1 月)。定位是全自主渗透 Agent 系统,README 专门有一节「Giving Agents Docker Without Giving Away the Host」,讲怎么给 Agent Docker 权限而不交出宿主机。部署走 docker compose,命令看仓库 Quick Start。最后提交 9 月 10 日。
CyberStrike(AGPL-3.0,2,811 星,建于 2026 年 2 月)。它不带模型,把你的 Claude、GPT 订阅接进来,README 写的是 「13+ specialized agents, 7,600+ security skills, and 120+ OWASP test cases」。这些数字是自报,我没有逐个核。安装一条:
npm i -g @cyberstrike-io/cyberstrike@latest && cyberstrike 老将 PentestGPT 还在,15,521 星,最后提交 7 月 14 日。7 月我核它 README 时,全自主模式依赖 Claude Code 和 Codex CLI,装它之前先确认这一条有没有变。
OpenAI 自己下场:codex-security
7 月新建的仓库,10,776 星,30 天涨 812。README 定位是 「a CLI and TypeScript SDK for defining security policy and finding, validating, and fixing security vulnerabilities」,也就是扫代码找洞、验证、修。
npm install @openai/codex-security npx @openai/codex-security login npx @openai/codex-security scan /path/to/directory 要求 Node.js 22.13.0 和 Python 3.10 以上。有一句话要看清:README 说 「Some cybersecurity requests and protected findings require approval through Trusted Access for Cyber」,意思是部分高危发现要走 OpenAI 的网络安全可信访问计划审批,入口是 chatgpt.com/cyber。你拿它扫自己的仓库没问题,扫出来的某些类别结果会被拦住等审批。
装在 Claude Code 上的红队技能包:Claude-Red、Agentic-Bug-Hunter、Claude-BugHunter
这一类是给 Claude Code 或 Codex 装的 SKILL.md 文件包,脱离宿主 Agent 单独跑不起来。
Claude-Red(MIT,6,213 星,建于 3 月)。README 原话:「Offensive security skills for Claude — drop-in SKILL.md files that turn Claude into a context-aware red team operator」。用例写得很明确:「authorized red team engagements, bug bounty triage, security research, CTF preparation」。最后提交 8 月 30 日。
Agentic-Bug-Hunter(MIT,4,986 星,建于 3 月)。定位是 「AI-powered bug bounty hunting toolkit that works with or without subscription」。它 9 月 19 日才首次进 bug-bounty 这个 topic 的 top30,README 首屏是品牌块,安装步骤在后面,自己看仓库。最后提交 9 月 17 日。
Claude-BugHunter(MIT,4,540 星,建于 5 月)。定位 「A Claude Code skill bundle for bug hunting and external red-teaming」,30 天涨 863 星。最后提交 9 月 18 日。
这三个技能包都是别人写好的 SKILL.md 文件,装进 Claude Code 就有执行权,装之前要先过一遍下一节的扫描工具。
装技能之前先扫技能:SkillSpector、agent-scan、AI-Infra-Guard、nono
技能包是代码,装进 Agent 就是给它执行权。9 月 17 日 AIR Security 公开的 Plugin4Shell(https://www.air.security/blog-posts/plugin4shell)就是这条链:Claude Code、Codex、GitHub Copilot、Gemini CLI 四款都受影响,插件市场按 commit 固定版本,但 Agent 不校验 checkout 到的是不是那个 commit。Anthropic 6 月 17 日修在 2.1.179,OpenAI 8 月 12 日修在 0.146.0,Copilot 到发稿没修,Google 回复不修。
下面四款就是做这件事的:两款扫技能文件,一款扫 MCP 配置和技能文件,一款管 Agent 的执行路径。
SkillSpector(NVIDIA,Apache-2.0,17,782 星,建于 3 月)。README 一句话:「Security scanner for AI agent skills. Detect vulnerabilities, malicious patterns, and security risks before installing agent skills.」,它是 NVIDIA Verified Skills 流水线的一部分。安装:
uv tool install git+https://github.com/NVIDIA/skillspector.git snyk/agent-scan(Apache-2.0,3,066 星)。前面提过,一条 uvx 命令扫 MCP 配置或 SKILL.md,不用装。
AI-Infra-Guard(腾讯,Apache-2.0,6,453 星)。5 月表里的老将,这 4 个月加了技能扫描:pip install aig-skill-scan。
nono(Apache-2.0,4,132 星,建于 1 月)。它管的是 Agent 的执行路径,技能文件归上面三款,定位「secure multiplexed execution paths for agents - zero trust」。装法 brew install nono,然后给 Agent 套一层:nono run --profile opencode -- opencode。README 提醒 1.0 之前 API 还会变。
顺序是先用 agent-scan 或 SkillSpector 扫技能文件,扫完没有告警再装 Claude-Red 这类技能包,装完用 nono 给 Agent 的执行路径套一层。
Agent 审计与对齐审查:iFixAi、Inspect、Inspect Petri、langwatch
渗透工具回答的是「它有没有洞」,这一类回答的是另一个问题:它有没有在干该干的事。
iFixAi(Apache-2.0,15,582 星,建于 4 月,60 天涨 13,956)。README 开头就划清界限:现有的评估、红队和可观测工具评的是技术指标,它评的是 「Is the agent doing the job it is supposed to do based on the business KPIs and Organizational Structure?」。所以别把它当渗透工具装。运行三种方式,最省事的是向导:
pip install "ifixai[<provider>]" ifixai setup ifixai run Inspect(英国 AI 安全研究所,MIT,2,808 星)。定位 「a framework for large language model evaluations」,自带 200 多个预置评测。安装看 inspect.aisi.org.uk。
Inspect Petri(MIT,1,339 星,3.0 版)。建在 Inspect 上的对齐审计 Agent,README 说它做四件事:按你的种子指令生成审计场景,用一个审计模型和一个目标模型跑多轮,模拟工具调用和回滚,最后用裁判模型按统一评分表打分。开源项目里把对齐审计做成审计模型、目标模型、裁判模型三方可跑流程的,目前我只找到它这一个。
langwatch(Apache-2.0,4,816 星,30 天涨 1,318)。定位 「trace, test, route and govern every LLM call in your company」。它有一条我觉得实用的命令,直接追踪你的编码 Agent:
npx langwatch claude # 或 codex、copilot、opencode 自托管一条 npx @langwatch/server,只要 Node.js,生产环境的部署方式看它的 Self-hosting 文档,README 里给了链接。
模型评估老将:promptfoo、deepeval、langfuse、opik、garak、PyRIT、deepteam
评估侧的老将大多还活着,按活跃、观察、停更三档排。
npm install -g promptfoopromptfoo init --example getting-started → promptfoo eval | ||||
pip install -U deepeval | ||||
pip install -U garakpython3 -m garak --target_type huggingface --target_name gpt2 --probes dan.Dan_11_0 | ||||
pip install pyrit | ||||
pip install -U deepteam | ||||
pip install agentdojopython -m agentdojo.scripts.benchmark -s workspace ... | ||||
ragas 有 15,769 星,但今年 2 月 24 日之后没有提交,按同一口径归停更。HarmBench 最后提交在 2024 年 8 月 16 日,当基准数据集用可以,2024 年之后新出现的攻击类型它没有收录。
garak 还是这一档里最容易上手的,7 月我按它的 README 核过,跑 HF 本地模型连 key 都不用。PyRIT 是框架,README 没有单行 quickstart,得写 orchestrator 和 target 的编排代码。
有人开始反制:AgentCapture
这个仓库 9 月才建,只有 111 星,写进来的原因是方向,热度还谈不上。
AgentCapture 是国产项目,AGPL-3.0,自述是「针对 AI 自动化渗透 Agent 的新一代反制蜜罐」,核心是「AI Agent 反制闭环:23 种主流 Agent 产品指纹识别(Claude Code / ChatGPT Codex / Kimi Cod…)」,手段包括用反代把 API 密饵塞进真实业务、反向提示词注入。
也就是说,上面那些自主渗透 Agent 一旦被用在未授权目标上,对面已经有人在按产品指纹做识别和反制,这个仓库我会隔一个月再拉一次数据看它有没有长起来。
7 月那篇论文的数字
7 月 13 日 arXiv 上有一篇《Baselines Before Architecture: Evaluating Coding Agents for Autonomous Penetration Testing》(https://arxiv.org/abs/2607.13085),作者 Ananda Dhakal、Krish Neupane、Aarjan Chaudhary。9 月 17 日 FreeBuf 有中文转述(https://www.freebuf.com/articles/ai-security/501522.html),标题说裸 Codex 抹平了专用框架的 benchmark 优势。我读了原文,转述里的两个百分比和论文表格对不上,下面全部用论文表格的数字。
基准是 XBOW validation benchmarks,104 道容器化 Web 漏洞题。被测是三个没做任何安全改造的编码 Agent:Codex、OpenCode、Pi。对照是两个专用渗透框架:MAPTA 和 PentestGPT V2。
作者的结论原句是:「Security harnesses can add benchmark lift and may improve cost efficiency, but their contribution should be measured against strong, model-matched plain-agent baselines and separated from backbone model progress.」
换成选型的话说,框架可能加分,但要拿同一个模型的裸 Agent 当基线去比,模型从 GPT-5 换到 GPT-5.5 带来的 22 个百分点不能算到框架头上。
论文没说的三件事
论文第七章 D 节自己列了局限,我挑三条和选型直接相关的。
一,Codex 和 OpenAI 的模型是配套设计的,其他 CLI 配 GPT 未必有这个成绩,配 Claude 或 Gemini 的数字论文没测。二,每个配置只跑了两轮,pass@2 就是把两轮的通过并起来算,样本很小。三,104 道题里作者修复了大约 40 个靶标才能跑,而且这是公开基准,训练数据里可能见过。
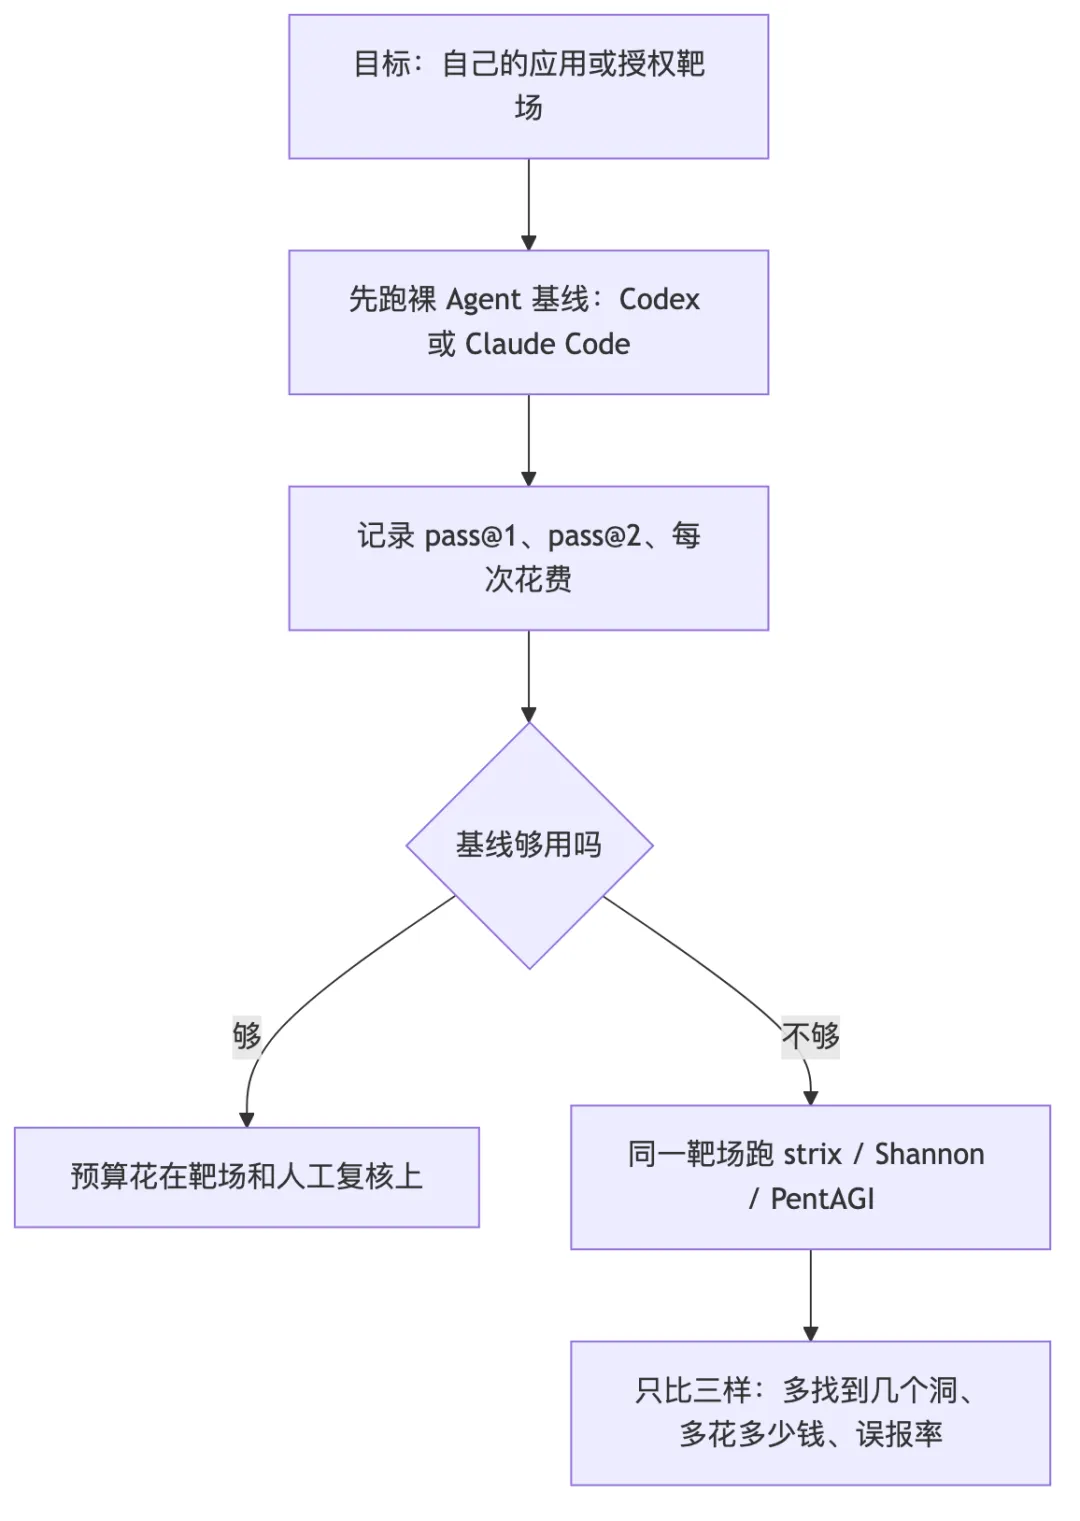
所以这篇论文能拿来做的事只有一件:在你自己的靶场上,先跑一遍裸 Codex 或裸 Claude Code,记下 pass@k 和花费,再决定要不要上 strix 或 Shannon。流程是这样:
OWASP 四个标准各对应哪些工具
9 月 17 日 FreeBuf 有一篇整理 OWASP 的 Agent 标准族(https://www.freebuf.com/articles/ai-security/501513.html),四个标准的职责按那篇转述是:AOS 负责观测与溯源,把 Agent 执行过程转成可观测的 trace;ACS 负责运行时裁决,对每次行为做 deny、proceed 或 approve;AISVS 是三级验证清单;AST10 把技能风险分成 10 类。OWASP 原页我没有逐条核,以下对应关系是我按各工具 README 自述的功能画的。
这张表的用法是反着看:你手上已经有 langfuse,AOS 这一栏就不用再买;你什么都没有,先补 AST10 那一栏,9 月 17 日的 Plugin4Shell 已经证明技能和插件是现在最容易被人塞东西的入口。
半小时能跑起来的顺序
7 月我按各家 README 核过一批安装步骤,当时排出的可上手顺序是 garak、ModelScan、AiSOC、NeMo Guardrails、PyRIT、CAI。这次新上榜的也没有逐个装跑,按 README 写的安装动作分三档,供你估时间。
一条命令就能跑,不用写配置:Shannon(npx)、codex-security(npx)、CyberStrike(npm 全局装)、langwatch(npx)、snyk/agent-scan(uvx)、garak(pip)、deepteam(pip)、deepeval(pip)、agentdojo(pip)、AiSOC(npx aisoc triage --demo,零 key)。
装完还要写配置或编排代码:PyRIT、CAI(pip install cai-framework)、Inspect、iFixAi(向导模式已经算简单的)、promptfoo(要写 promptfooconfig)。
要起容器或集群:PentAGI(docker compose)、open-kritt(自托管)、AI-Infra-Guard 完整平台。
技能文件,装进 Claude Code 就能用:Claude-Red、Claude-BugHunter、strix 的技能版。
43 款总表
strix --target ./app-directory | |||||
npx @keygraph/shannon@latest | |||||
npm install -g promptfoo | |||||
pip install -U deepeval | |||||
uv tool install git+https://github.com/NVIDIA/skillspector.git | |||||
pip install "ifixai[<provider>]" | |||||
pentestgpt --target <IP> --mode pentest | |||||
npx @openai/codex-security scan <dir> | |||||
pip install cai-framework | |||||
pip install -U garak | |||||
pip install aig-skill-scan | |||||
npx langwatch claude | |||||
pip install pyrit | |||||
brew install nono | |||||
uvx snyk-agent-scan@0.5.17 <file> | |||||
pip install -U deepteam | |||||
npm i -g @cyberstrike-io/cyberstrike@latest | |||||
pip install agentdojo | |||||
表里的星数和提交日期是 9 月 19 日的,命令照抄各仓库 README,以你装的那天为准。
附录:43 款工具地址
按类别排,地址都是 GitHub 仓库首页,命令和 license 以你打开那天的 README 为准。
自主渗透 Agent 与渗透框架
usestrix/strix:https://github.com/usestrix/strix KeygraphHQ/shannon:https://github.com/KeygraphHQ/shannon vxcontrol/pentagi:https://github.com/vxcontrol/pentagi CyberStrikeus/CyberStrike:https://github.com/CyberStrikeus/CyberStrike Armur-Ai/Pentest-Swarm-AI:https://github.com/Armur-Ai/Pentest-Swarm-AI GreyDGL/PentestGPT:https://github.com/GreyDGL/PentestGPT aliasrobotics/cai:https://github.com/aliasrobotics/cai 0x4m4/hexstrike-ai:https://github.com/0x4m4/hexstrike-ai shinthink/blitzstrike:https://github.com/shinthink/blitzstrike
代码漏洞扫描与研究
openai/codex-security:https://github.com/openai/codex-security Kritt-ai/open-kritt:https://github.com/Kritt-ai/open-kritt
红队技能包
SnailSploit/Claude-Red:https://github.com/SnailSploit/Claude-Red awarexone/Agentic-Bug-Hunter:https://github.com/awarexone/Agentic-Bug-Hunter elementalsouls/Claude-BugHunter:https://github.com/elementalsouls/Claude-BugHunter
技能、MCP 与执行路径扫描
NVIDIA/SkillSpector:https://github.com/NVIDIA/SkillSpector snyk/agent-scan:https://github.com/snyk/agent-scan Tencent/AI-Infra-Guard:https://github.com/Tencent/AI-Infra-Guard nolabs-ai/nono:https://github.com/nolabs-ai/nono splx-ai/agentic-radar:https://github.com/splx-ai/agentic-radar slowmist/MCP-Security-Checklist:https://github.com/slowmist/MCP-Security-Checklist
Agent 审计与对齐审查
ifixai-ai/iFixAi:https://github.com/ifixai-ai/iFixAi UKGovernmentBEIS/inspect_ai:https://github.com/UKGovernmentBEIS/inspect_ai meridianlabs-ai/inspect_petri:https://github.com/meridianlabs-ai/inspect_petri langwatch/langwatch:https://github.com/langwatch/langwatch
模型与应用红队
NVIDIA/garak:https://github.com/NVIDIA/garak microsoft/PyRIT:https://github.com/microsoft/PyRIT confident-ai/deepteam:https://github.com/confident-ai/deepteam msoedov/agentic_security:https://github.com/msoedov/agentic_security cyberark/FuzzyAI:https://github.com/cyberark/FuzzyAI utkusen/promptmap:https://github.com/utkusen/promptmap meta-llama/PurpleLlama:https://github.com/meta-llama/PurpleLlama ethz-spylab/agentdojo:https://github.com/ethz-spylab/agentdojo centerforaisafety/HarmBench:https://github.com/centerforaisafety/HarmBench microsoft/AI-Red-Teaming-Playground-Labs:https://github.com/microsoft/AI-Red-Teaming-Playground-Labs
评估与可观测
promptfoo/promptfoo:https://github.com/promptfoo/promptfoo confident-ai/deepeval:https://github.com/confident-ai/deepeval langfuse/langfuse:https://github.com/langfuse/langfuse comet-ml/opik:https://github.com/comet-ml/opik vibrantlabsai/ragas:https://github.com/vibrantlabsai/ragas
网关
BerriAI/litellm:https://github.com/BerriAI/litellm Portkey-AI/gateway:https://github.com/Portkey-AI/gateway protectai/llm-guard:https://github.com/protectai/llm-guard
反制
Tcotl/AgentCapture:https://github.com/Tcotl/AgentCapture
文中引用的报告与论文
《Baselines Before Architecture》论文:https://arxiv.org/abs/2607.13085 AIR Security 的 Plugin4Shell 公告:https://www.air.security/blog-posts/plugin4shell FreeBuf 对论文的转述:https://www.freebuf.com/articles/ai-security/501522.html FreeBuf 整理的 OWASP Agent 标准族:https://www.freebuf.com/articles/ai-security/501513.html 本号 5 月那篇《AI 红队工具怎么选?6 类 18 款对比》
免责与下一步
本文所有工具仅用于授权范围内的安全测试、自查和修复验证。在他人系统未经授权运行,等同非法入侵,法律责任自负。
你现在能做的三件事:把自己在用的工具对照总表标出停更项;在自己的靶场跑一遍裸 Codex 或 Claude Code,记下 pass@k 和花费;装任何技能包之前,先用 agent-scan 或 SkillSpector 扫一遍。
5 月那张表我留着,下一次复盘定在 2027 年 1 月,到时候再拉一遍这 43 个仓库的 pushed_at。